Research · 2022 – 2023
Side-channel and fault attacks on embedded targets
Grenoble INP Esisar
Correlation power analysis on STM32, RSA and clock-glitching experiments in the embedded security lab.
Hardware securitySTM32CPAFault injection
Overview#
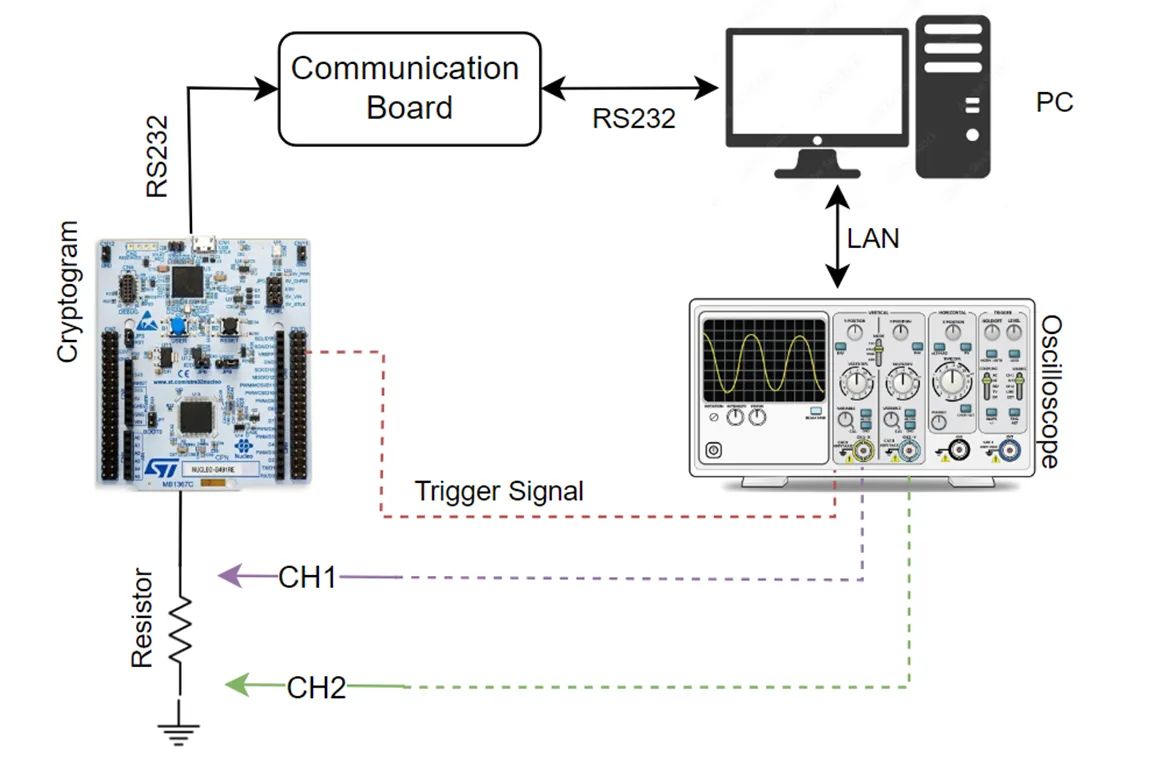
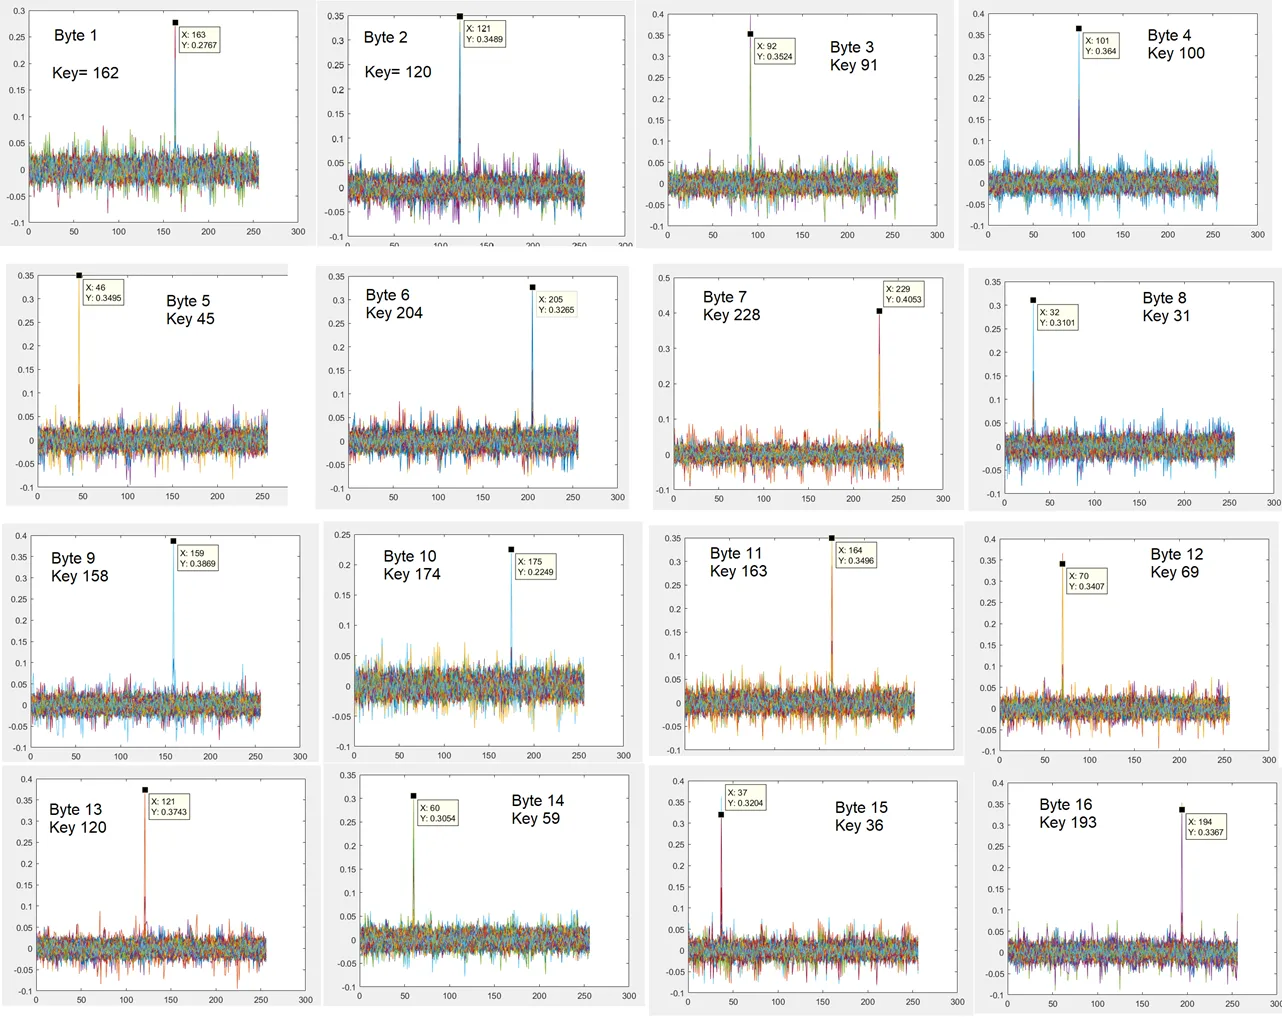
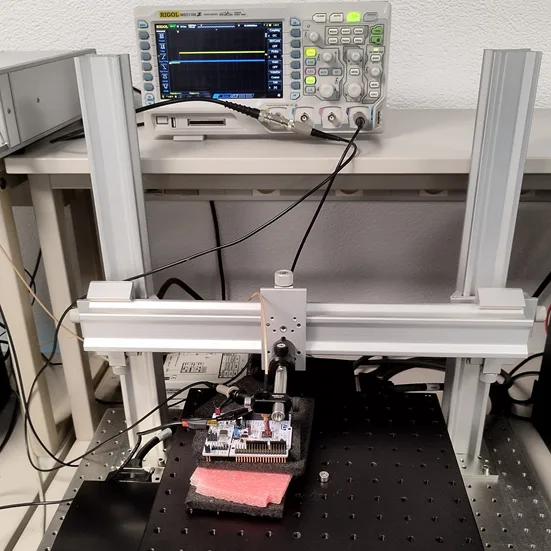
Hands-on experiments using Correlation Power Analysis (CPA) on an AES implementation written in C and running on an STM32 ARM microcontroller. The goal was to study the AES algorithm and the STM32 Nucleo board, propose a measurement method, capture power traces with an oscilloscope, and complete the attack by running CPA on the captured traces.
Steps#
- Preparing the Nucleo board for a CPA attack
- Focusing the attack on the point of maximum leakage
- Interfacing the AES implementation with the computer
- Performing the attack with a MATLAB script
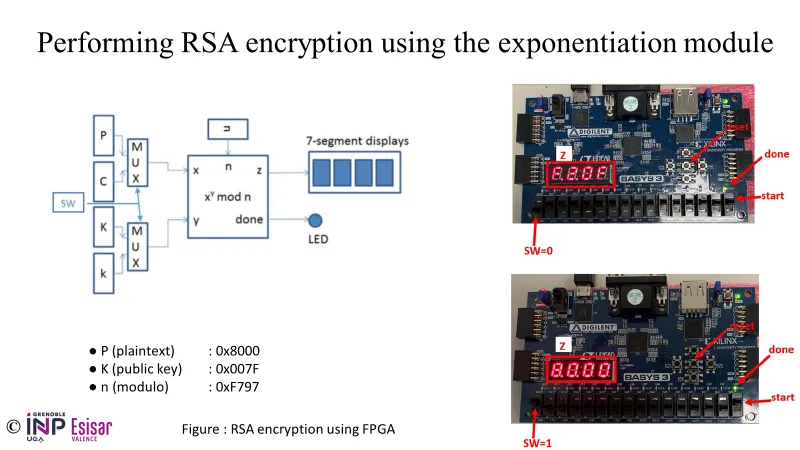
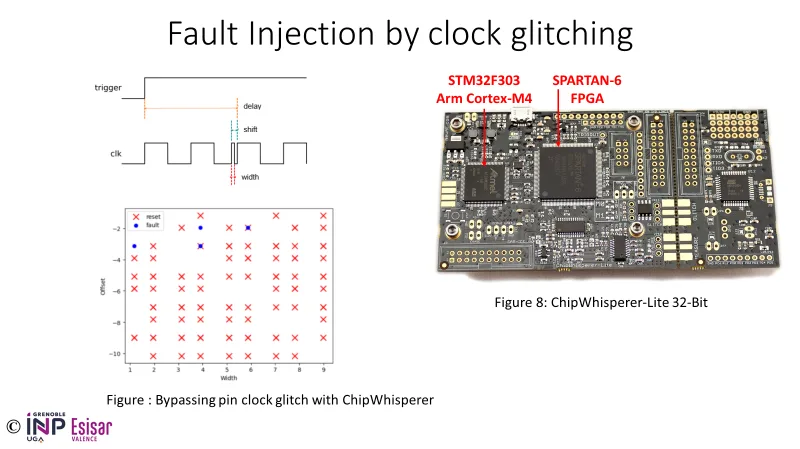
The lab also covered RSA encryption on an FPGA using an exponentiation module, and fault injection by clock glitching with a ChipWhisperer-Lite (STM32F303 and Spartan-6 targets).
Grenoble INP Esisar, France.
Figures